
Potential Reentrancy
An external call occurs before the balance is updated. Review the order of operations
Smart contract security, brought into focus. Identify potential vulnerabilities, understand the connections, and turn findings into action
For developers, digital-asset businesses & financial institutions
Precision & recall
on evaluated benchmarks
Smart contracts in
the evaluated datasets
To adapt to new
partner artefacts
A bounded integration
and adoption pathway
Precision and recall were measured on evaluated smart-contract vulnerability benchmark datasets. Results vary by vulnerability class and partner artefacts. Technology is patent-pending
THE PLATFORM
Connect the finding to the code that matters. Mando Scan brings vulnerability detection, graph analysis and remediation guidance into one assessment workflow
Understand the finding and trace the connection
Mapping contract relationships…
An external call occurs before the balance is updated. Review the order of operations
The return value of a low-level call is not checked. Handle the failure path explicitly
21 function withdraw() external {
22   uint amount = balances[msg.sender];
23   require(amount > 0);
24   (bool ok, ) = msg.sender.call
25     {value: amount}("");
26   require(ok);
27   balances[msg.sender] = 0;
28 }

37 function pay(address to) external {
38   to.call{value: fee}("");
39 }
Findings mapped to relevant source lines
Relationships between functions, calls and state make the security context easier to explore
Potential risk pathVault.sol · Sample report
FINDINGS + EVIDENCE + GUIDANCEFind vulnerabilities at contract and source-line level
Explore code relationships through graph insights
Give developers clear fix guidance and a report
The Technology
Smart contracts are systems of connected logic. Mando Scan combines graph-based analysis and AI to help reveal potential vulnerabilities within those relationships
Represent code structure and dependencies as a graph, so findings have context
Apply research-driven models to identify potential issues and locate affected code
Bring findings, evidence and remediation guidance together for security review
Built For Performance
Move from smart contract source to focused findings, with context at every step
Start with Solidity source code and build a connected view of the contract’s structure and logic
Follow relationships between functions, calls and state to understand the context behind a potential vulnerability
Explore findings linked to source code, review suggested fixes, and bring the evidence together in an exportable report
BUILT FOR YOUR WORKFLOW
From a single contract to an institutional assessment programme, build a clearer view of technical risk
Support technical due diligence, internal security governance and regulatory-readiness programmes with documented smart contract findings
Technical assessments support preparation. They do not constitute regulatory approval or a guarantee of security
FROM ASSESSMENT TO ADOPTION
A bounded pathway from technical assessment to an adoption decision
Adapt the assessment to new partner artefacts and explore the first findings
Define scope, assess results and validate the workflow in your environment
PLANS FOR EVERY STAGE
Choose the level of graph insight and remediation support you need
For a focused first look
More scans with practical guidance
A deeper view of your code
Proposed USD pricing for team review. Free registration includes two scans. Final availability, billing and terms are to be confirmed
Explore a one-month pilot with up to 30 scans, subject to team verification. Discuss a 3, 6 or 12-month engagement, or a tailored scope
Discuss an institutional pilotProposed programme for review. Institutional package totals are being reconciled before publication
The People Behind The Platform
A team bringing together software security research, engineering and commercial experience to turn research into practical smart contract security
CTO
Research Assistant Professor
CMO & Investor Relations
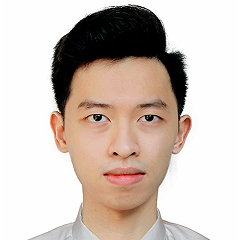
Engineering Lead
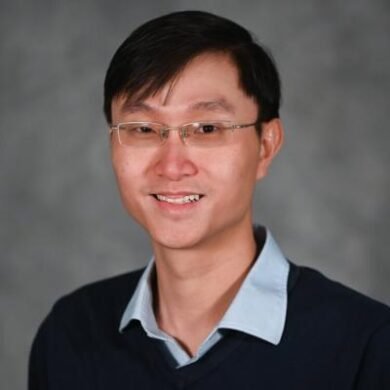
Technical Manager
RESEARCH FOUNDATION
Explore the research behind graph-based smart contract vulnerability detection
Patent-Pending Technology
PARTNER WITH MANDO SCAN
Connect your clients with AI-powered smart contract security assessments
Explore a partnershipA FEW MORE DETAILS
Need to discuss your specific environment?
Talk to our team
Mando Scan identifies potential smart contract vulnerabilities and provides technical findings, graph insights and remediation guidance. Assessments can support pre-deployment checks and ongoing security reviews
Technical findings may support internal governance, institutional due diligence and regulatory-readiness programmes. An assessment does not itself provide regulatory approval, certification or a guarantee that a contract is secure
Precision and recall above 95% were measured on evaluated smart-contract vulnerability benchmark datasets containing more than 1,600 contracts. Performance varies by vulnerability class and partner artefacts
Start with a scoped technical assessment or discuss an institutional pilot. The proposed pathway combines adaptation in minutes with a 30-day integration and adoption evaluation
LET’S BUILD WHAT’S NEXT
Tell us what you’re building. We’ll help define the right assessment or pilot
contact@mandoscan.com